SENTINEL
Autonomous Cyber Defense
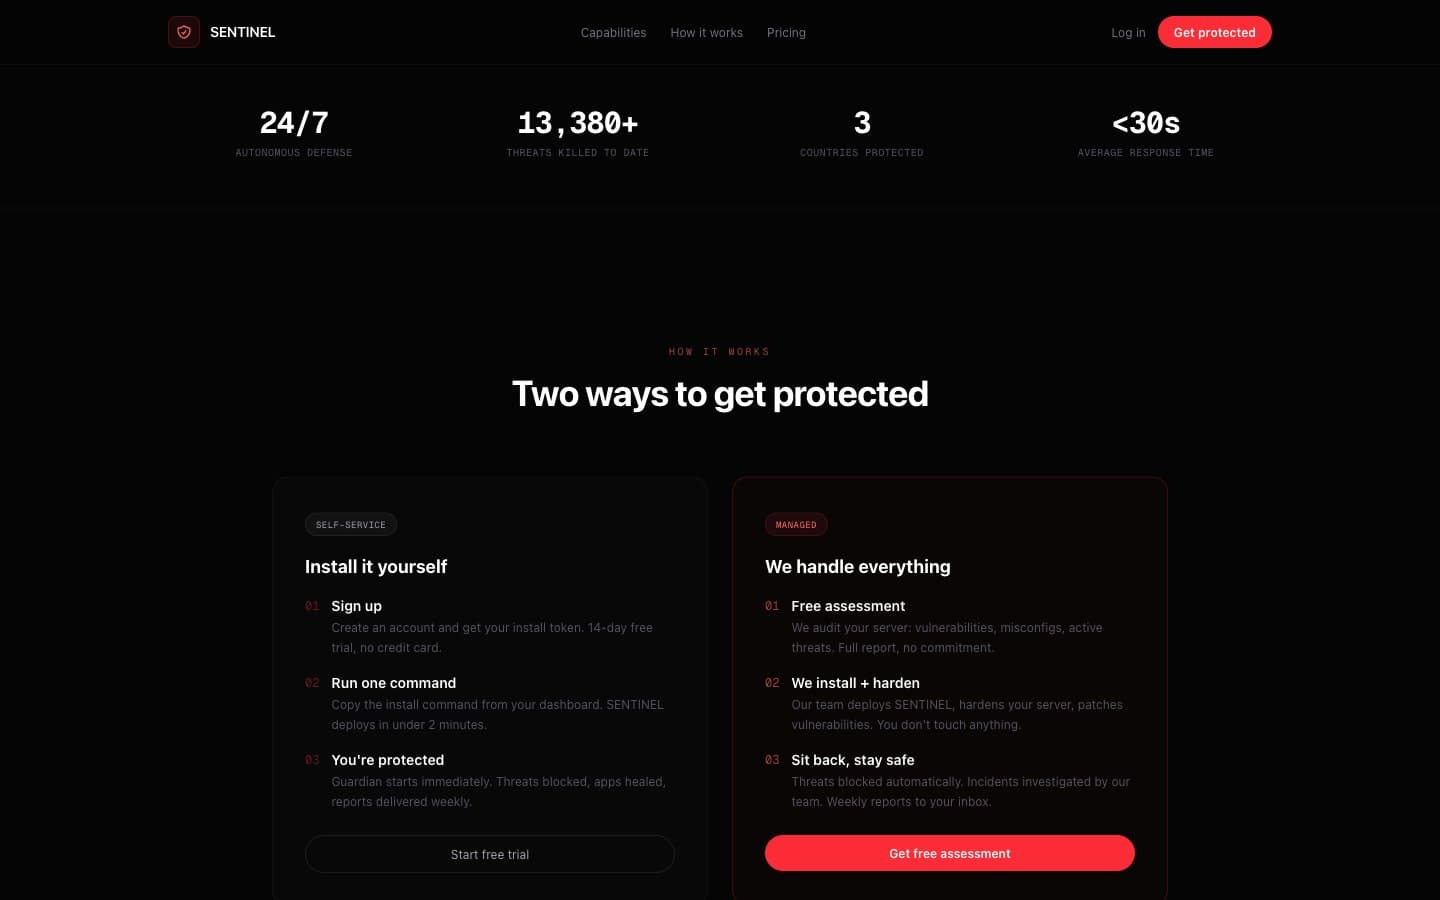
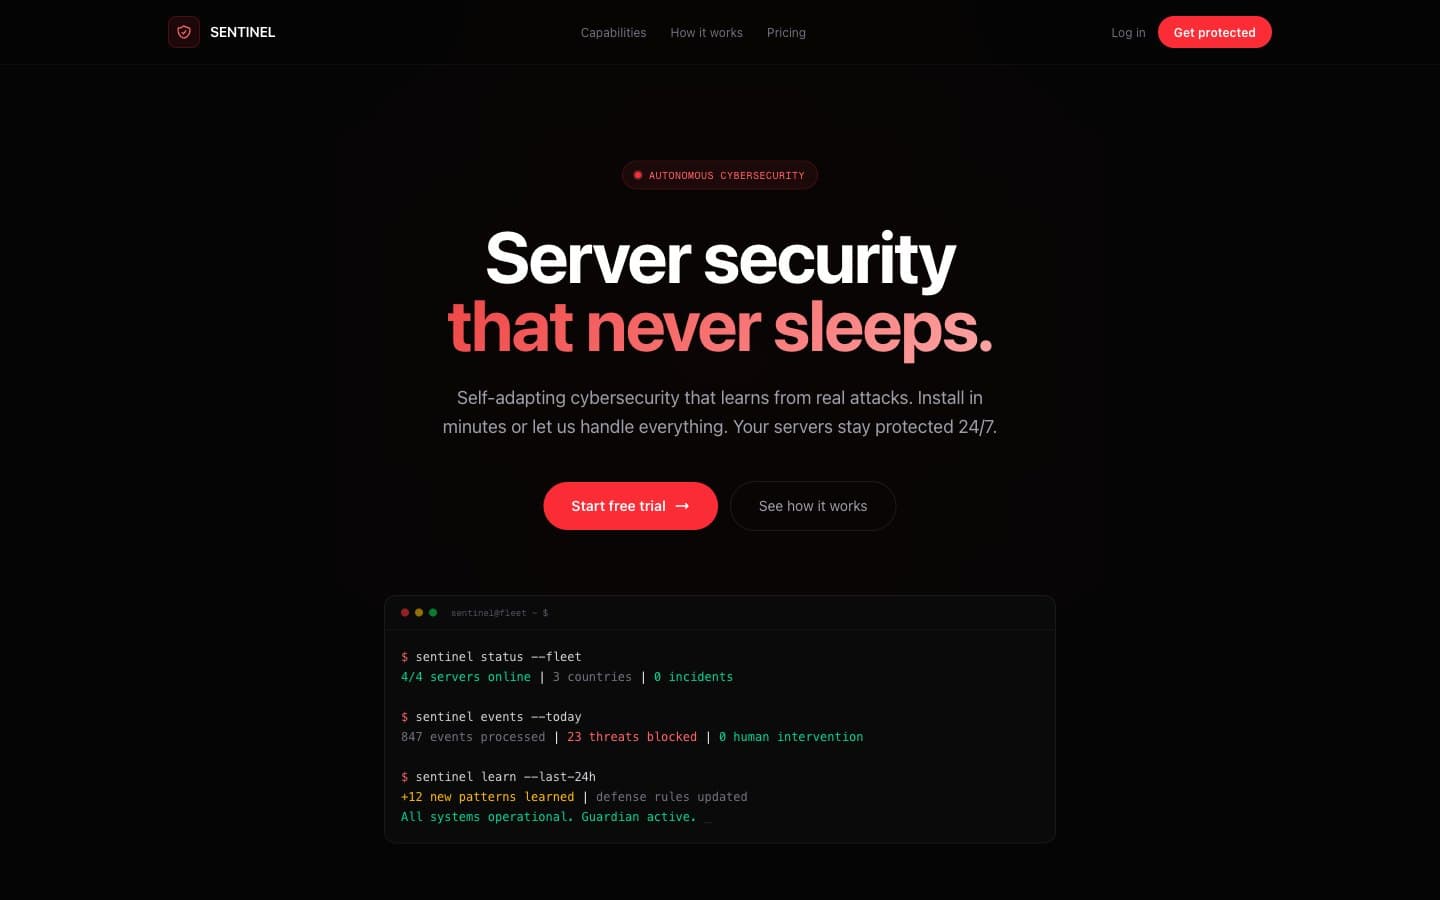
Self-adapting threat detection running on our own servers across three countries, every day since we deployed it. It learns from real attacks, blocks them, and heals compromised systems without anyone being woken up.
Challenge
Protecting a multi-server fleet across three countries from real-world attacks required 24/7 human monitoring, with threats evolving faster than manual response could handle.
Solution
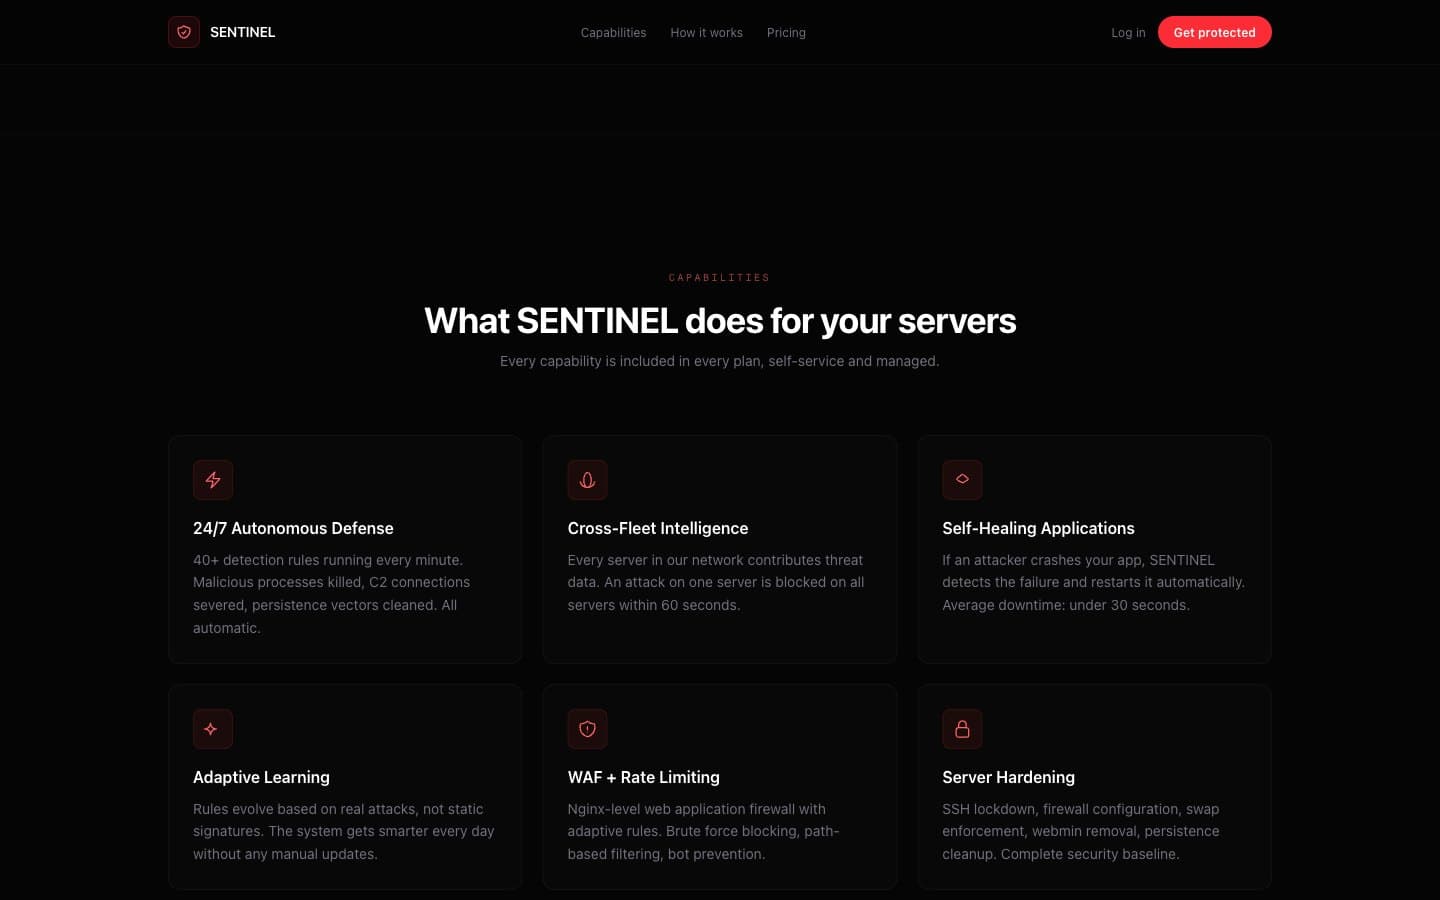
Created a self-adapting guardian that learns from every attack. Automated threat detection, IP blocking, process killing, persistence removal, and system healing. Deployed via a 3-location update system with hash-based self-update.
Impact
Thousands of events processed daily with zero human intervention. Self-updating across all servers. Learns from real attacks to strengthen defenses automatically.
Key features
3 countries, zero intervention
Real-time threat detection and auto-response
Self-adapting defense rules from attack patterns
3-location deployment with hash verification
Automated /dev/shm cleanup and process killing
IP blocking with intelligent rate limiting
Cross-fleet learning from all 4 servers
Screenshots
Inside the platform